Cybrolix GRC: the modern operating system for compliance
Implement local and international standards out of the box, automate risk assessments and policy campaigns, and give leadership a dashboard that answers "are we compliant?" in one glance.
Built-in support for local and international standards
GRC software should reduce the work of compliance, not add to it
Simplicity
Most GRC tools need weeks of training. Cybrolix is built so a new user can run a compliance project on day one.
Time and budget
Less time understanding the tool and less spend on professional services means more budget for actual security.
Plug and play
Regional and international regulations keep changing. Cybrolix ships with UAE IA, ISR, SAMA, NCA, ISO 27001 and more ready to use.
No manual work
Excel sheets and Word documents are replaced by automated tasks generated from the standard you choose.
Everything a compliance team needs, in one place
Implement standards straight out of the box
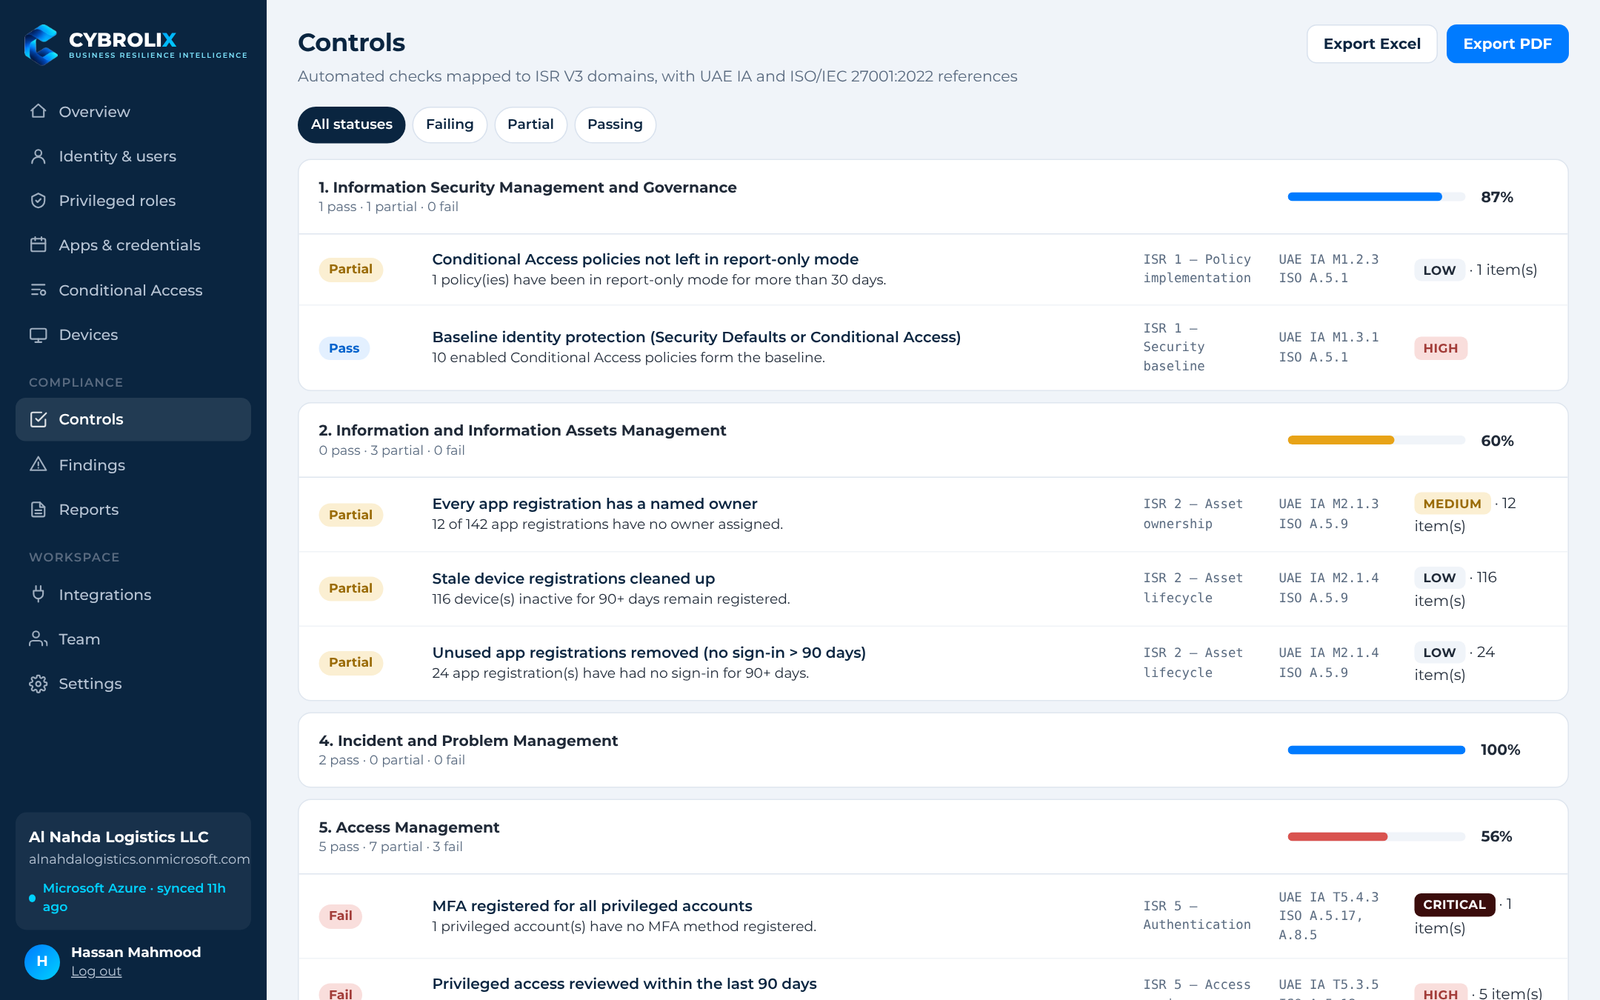
Choose a standard and Cybrolix generates the full control set, tasks and evidence requirements. No workflow configuration needed before you can start.
- Pick from NIST, ISO 27001, PCI DSS, UAE IA, ISR V3, SAMA CSF and many more
- Track implementation progress per control and per department
- Delegate ownership across the organisation with clear due dates
Risk assessments with minimal effort
Stop discovering and typing risks by hand. Cybrolix proposes risks from your findings and from a library of 3,000+ risks and mitigations.
- Use your own enterprise or cyber-security risk methodology
- Run assessments with the guided wizard or let automation suggest them
- Asset-, service- and scenario-based approaches supported
Policy acknowledgement campaigns in a few clicks
Upload or link a policy, choose the audience and send. Cybrolix tracks who has acknowledged, sends reminders and exports the results.
- Send acknowledgement links to employees and third parties
- Automatic reminders for anyone who has not responded
- Export results from the dashboard for your auditor
A library of 100+ standards, including your own
Start a project and pick the standard from a dropdown. If you have an internal framework or a client-specific one, upload it and Cybrolix turns it into trackable controls.
- Major Middle East standards: ISR, UAE IA, UAE PDPL, SAMA, NCA ECC, Qatar NIA
- International: ISO 27001, ISO 22301, SOC 2, NIST CSF, GDPR, DORA, NIS2
- Upload a custom standard and implement it within minutes
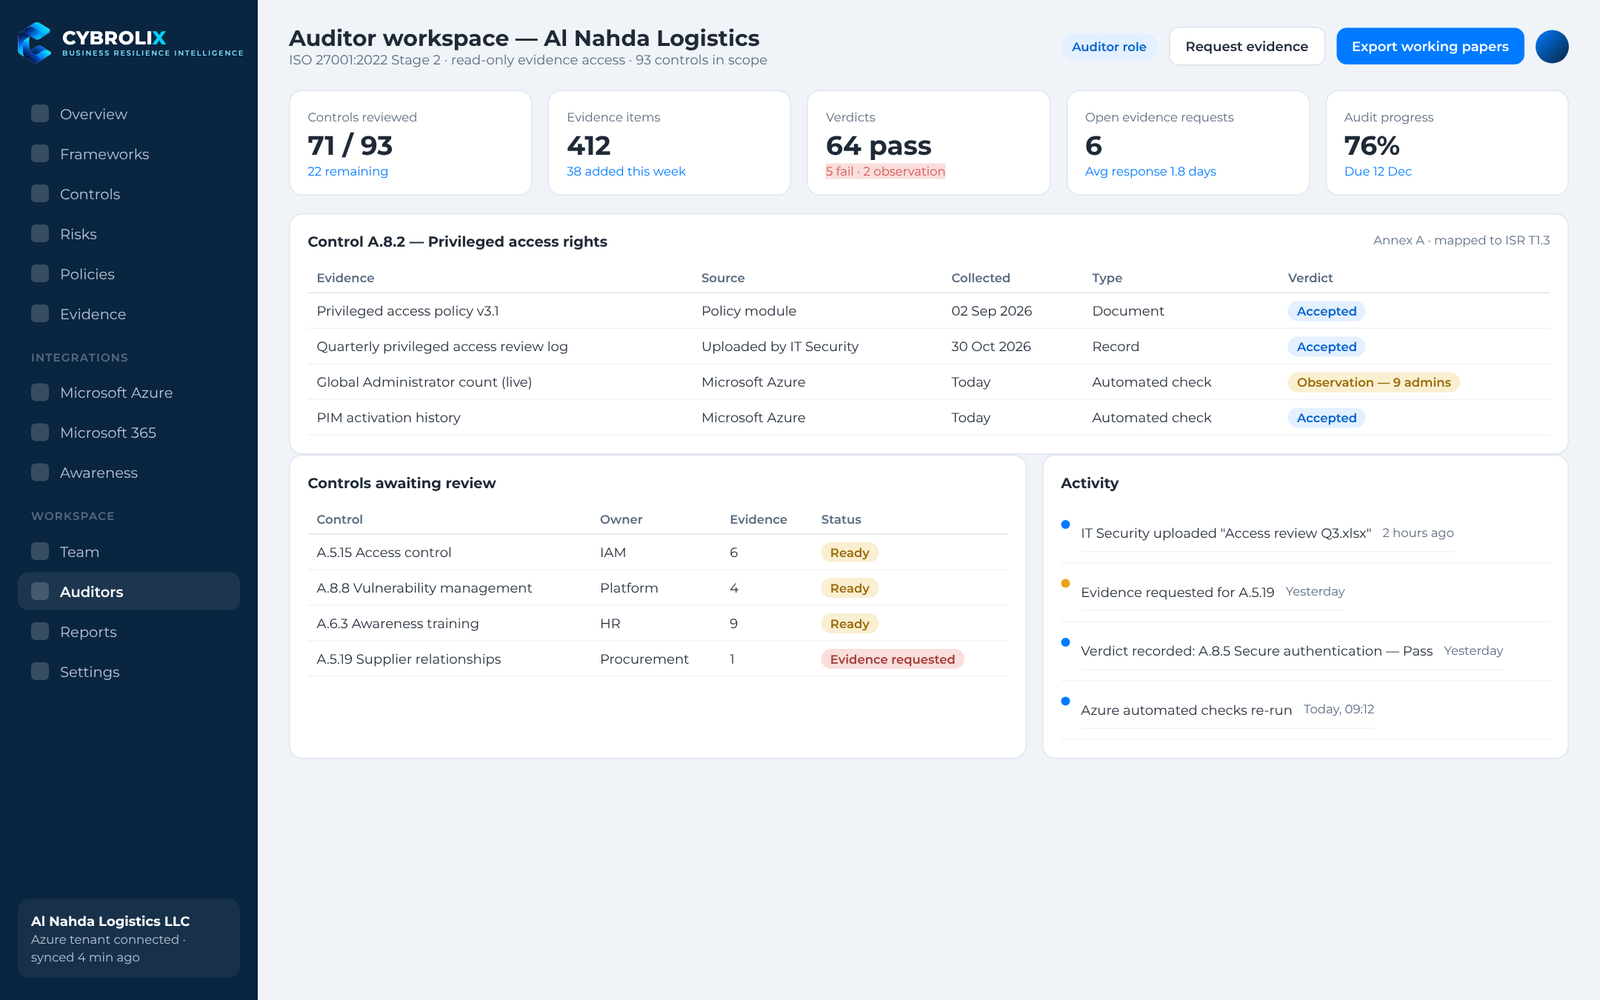
Dashboards that leadership and auditors both understand
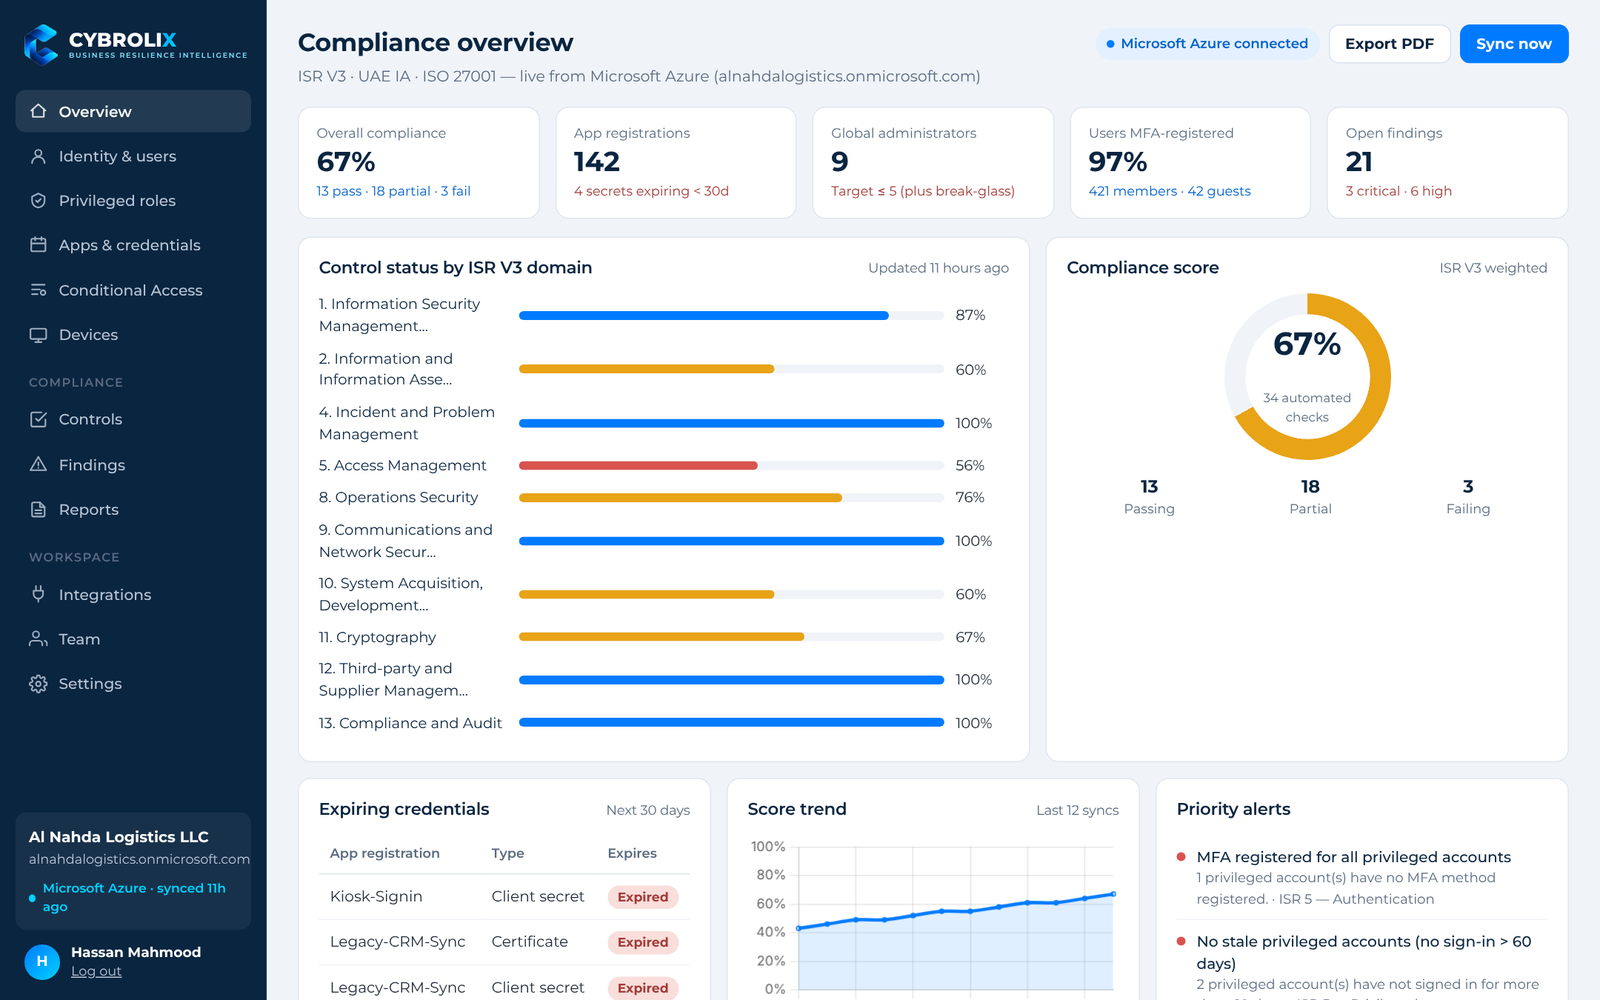
The global dashboard shows every framework, every owner and every outstanding task in real time.
- Filter by standard, implementation status, user or department
- Drill from a percentage down to the individual control and its evidence
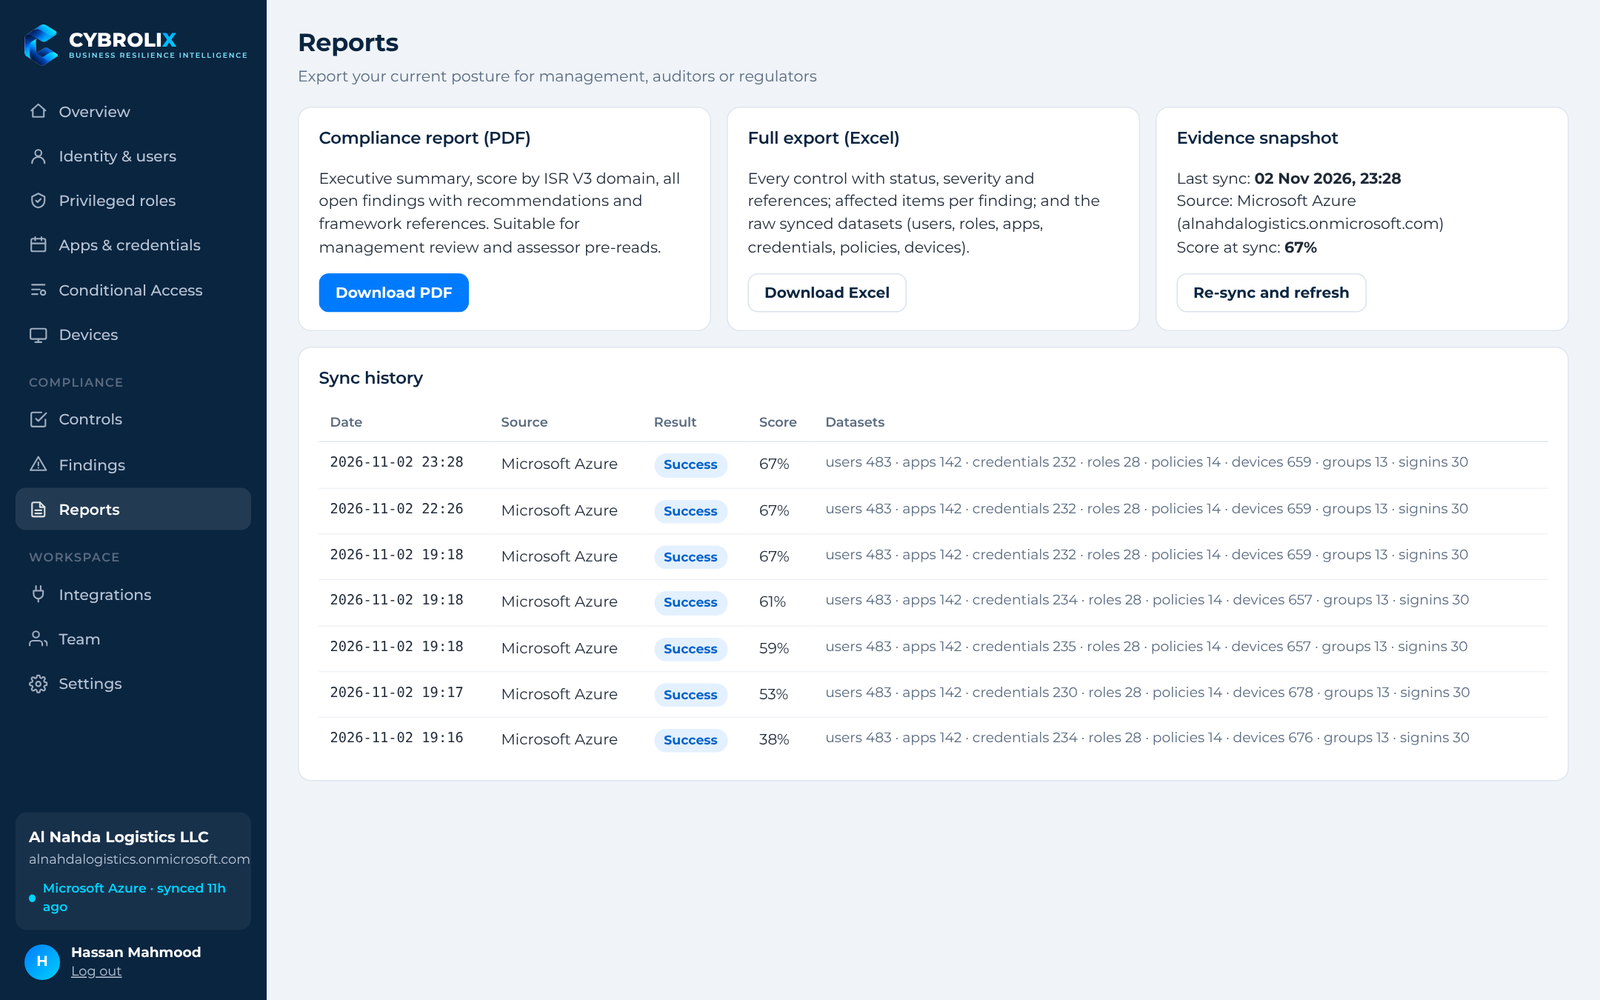
- Export any view to PDF or Excel
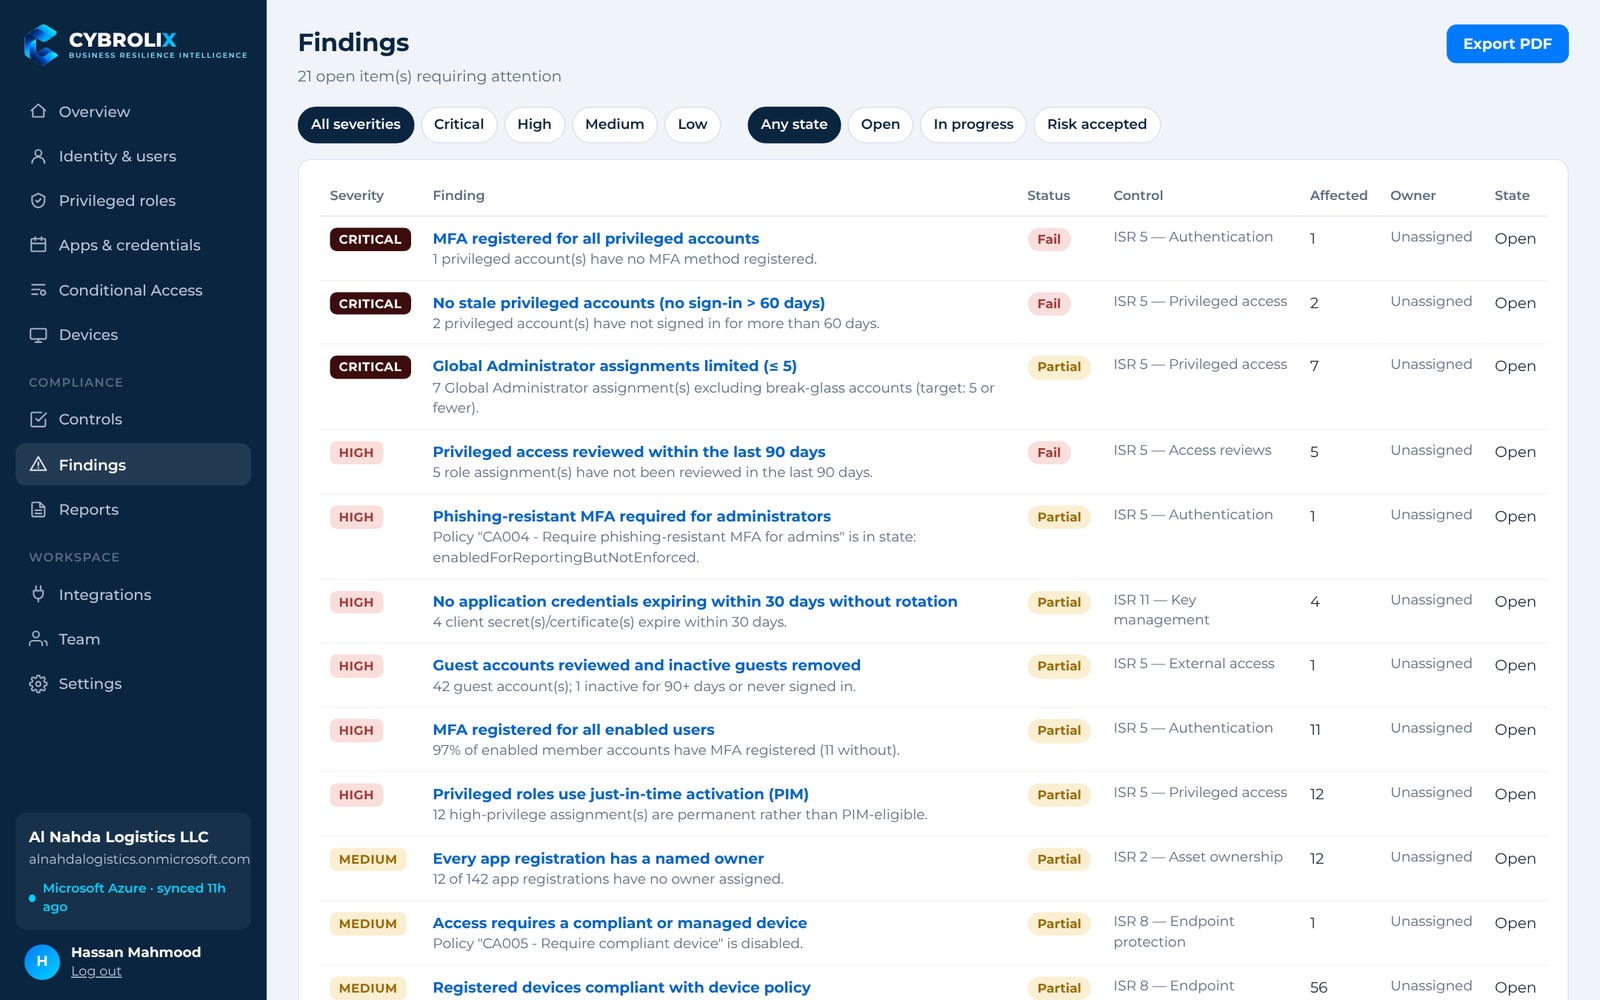
Connect Microsoft Azure for live technical evidence
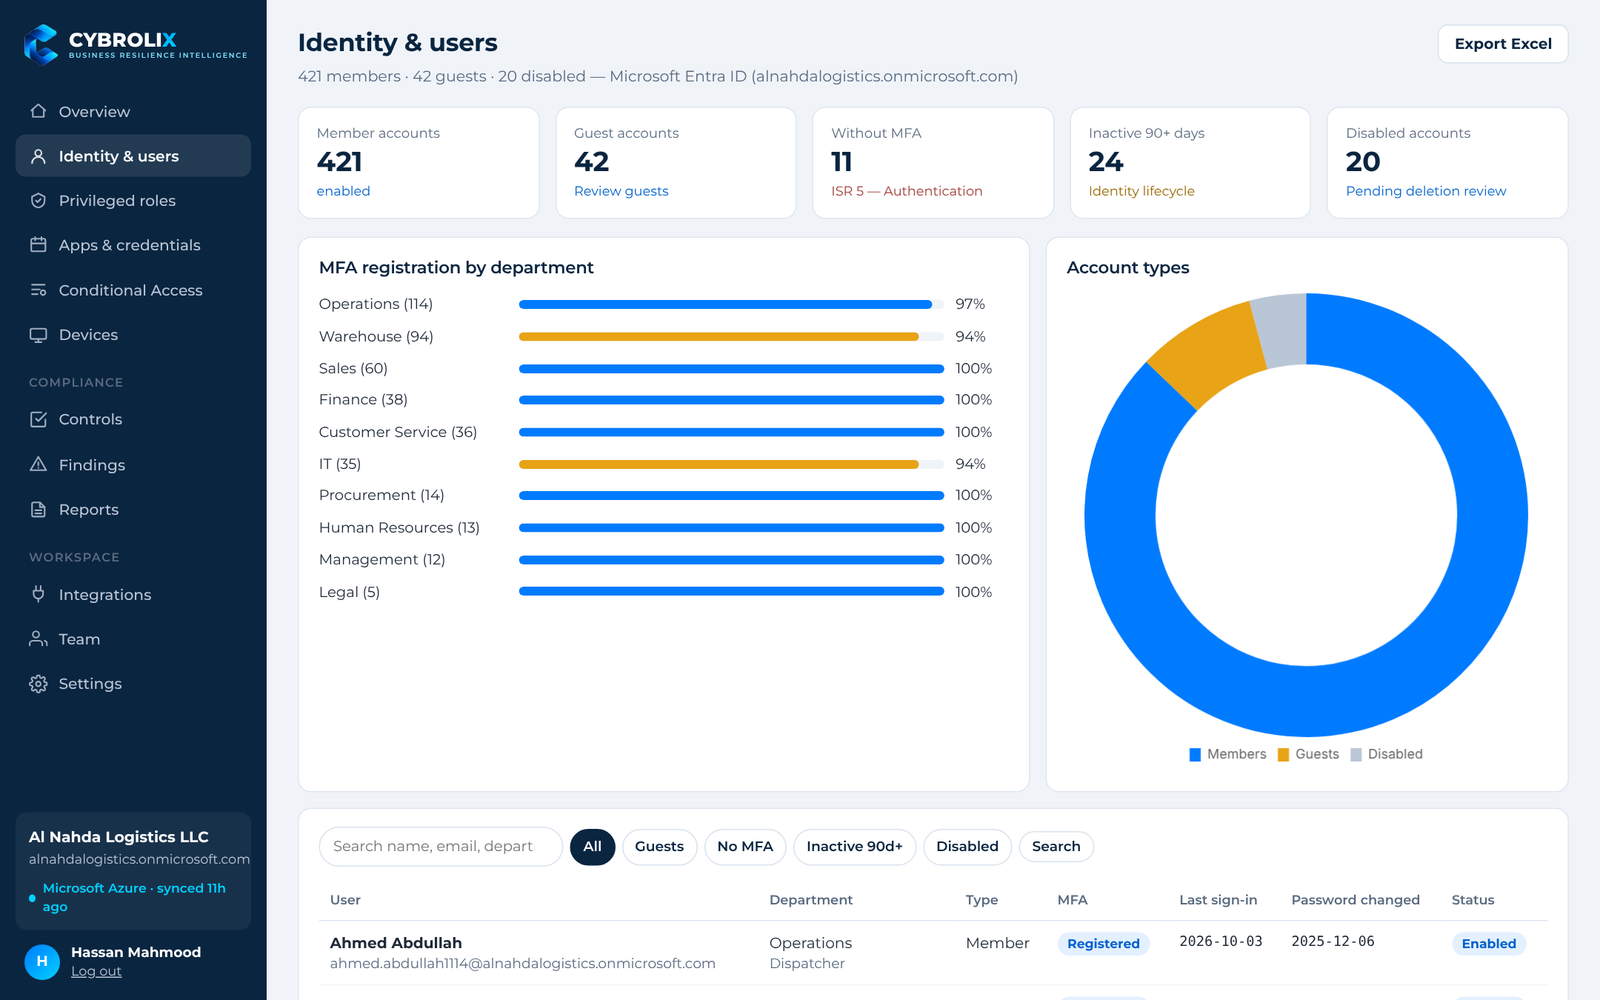
With read-only access to Microsoft Entra ID, Cybrolix checks identity and access controls continuously and maps the results to ISR and UAE IA.
- App registrations and expiring client secrets and certificates
- Directory roles, Global Admin count and privileged access reviews
- MFA registration, Conditional Access coverage, guest and stale accounts
From sign-up to audit-ready in four steps
Create your workspace
Register, add your organisation and invite the people who own controls.
Choose your frameworks
Pick ISR, UAE IA, ISO 27001 or any of 100+ standards. Controls are generated instantly.
Connect your systems
Link Microsoft Azure and your other tools so evidence is collected automatically.
Fix gaps, show progress
Work through findings with owners and share the live dashboard with your auditor.
Designed around ISR, UAE IA and the GCC regulatory landscape
Cybrolix is built in Dubai with the controls that regulators here actually ask about. Dubai's Information Security Regulation (ISR), the UAE IA standard and the UAE PDPL come pre-mapped, with technical checks that read directly from your cloud tenant.
Create your account
Frequently asked questions
Which standards does Cybrolix GRC support?
Over 100, including ISR V3, UAE IA, UAE PDPL, SAMA CSF, NCA ECC, Qatar NIA, ISO 27001, ISO 22301, SOC 2, NIST CSF, PCI DSS, GDPR, DORA and NIS2. You can also upload your own.
Do I need to install anything?
No. Cybrolix is cloud-based. Integrations such as Microsoft Azure use read-only API access that you authorise from your own tenant.
Can auditors access the platform?
Yes. You can invite your auditor with a restricted role so they see evidence and progress without editing anything.
How long does it take to get started?
Creating a workspace and generating your first control set takes minutes. Connecting Azure takes a few more clicks. The time to full compliance depends on the gaps we find together.
Put your GRC programme on autopilot
Create your Cybrolix account, choose a framework and see your first compliance dashboard today.