What ISR V3 actually asks of Dubai organisations
Dubai's Information Security Regulation is often described as "ISO 27001 for government". That is only half tr...
Cybrolix is the GRC and compliance automation platform that connects to Microsoft Azure, maps what it finds to ISR, UAE IA, ISO 27001 and other frameworks, and keeps your controls, risks and policies audit-ready every day — not just before the auditor arrives.
Built-in support for local and international standards
Meet the Dubai Electronic Security Center's Information Security Regulation with control-by-control visibility.
Learn more →
Implement the UAE Information Assurance standard for government and critical-sector entities.
Learn more →
Operate an ISMS that stays certified year-round, with evidence gathered as you work.
Learn more →
Protect personal data and demonstrate privacy compliance across jurisdictions.
Learn more →
SAMA, NCA ECC, DORA, NIS2 and more — pre-mapped so you start from a finished control set.
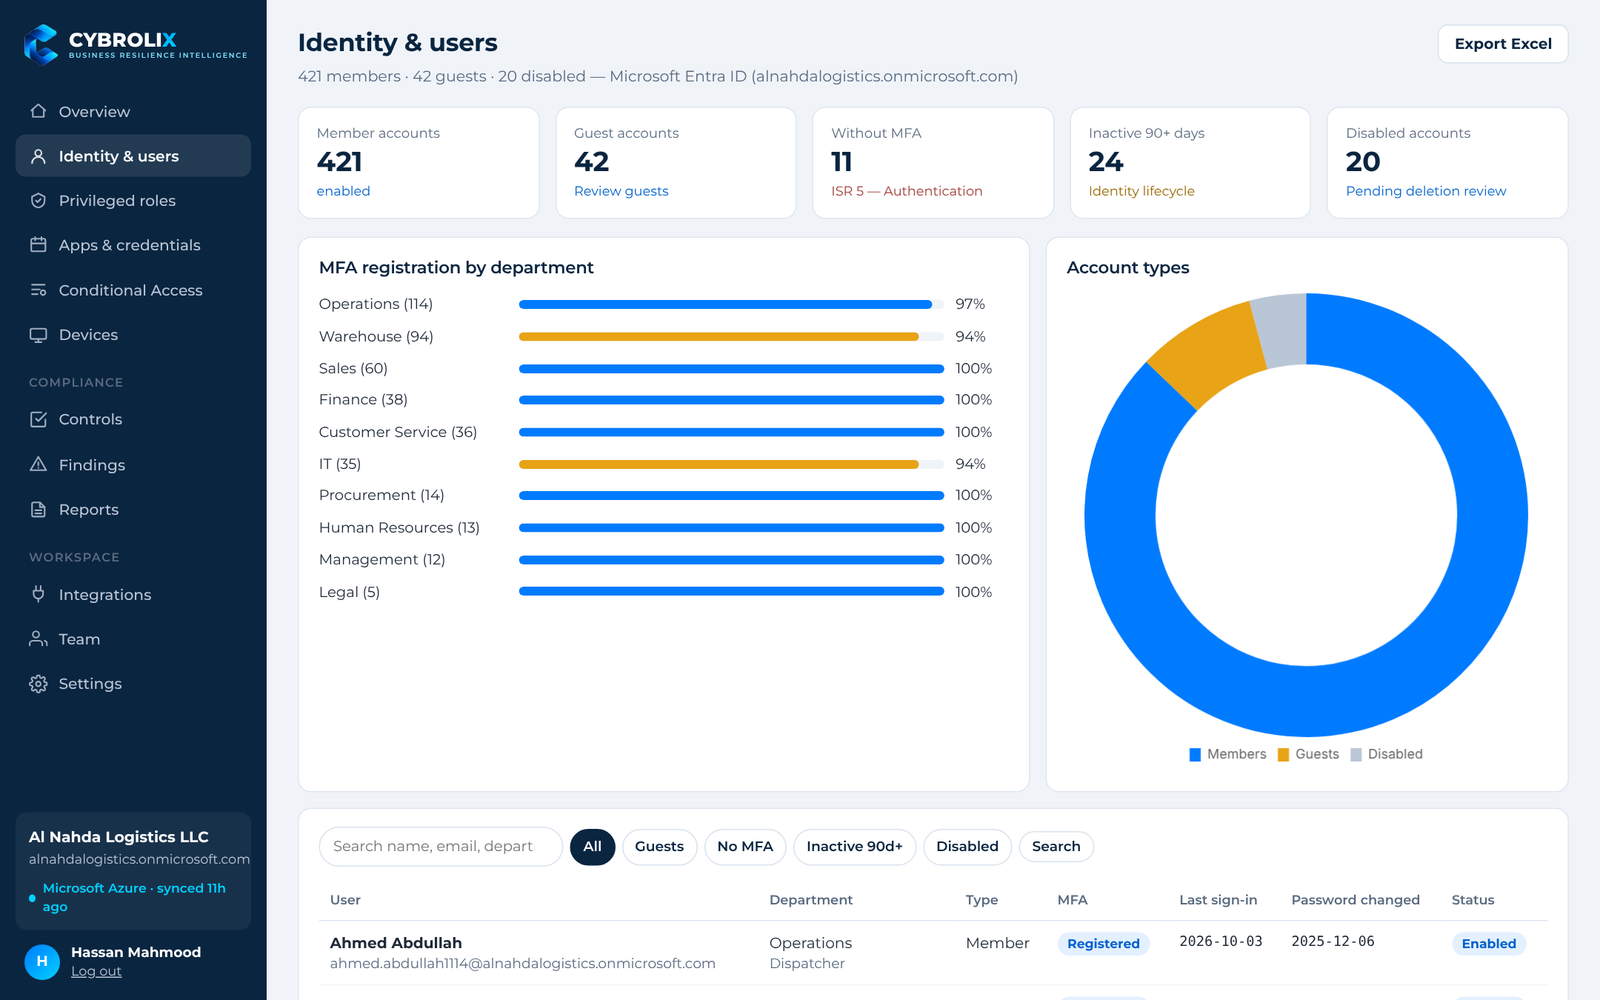
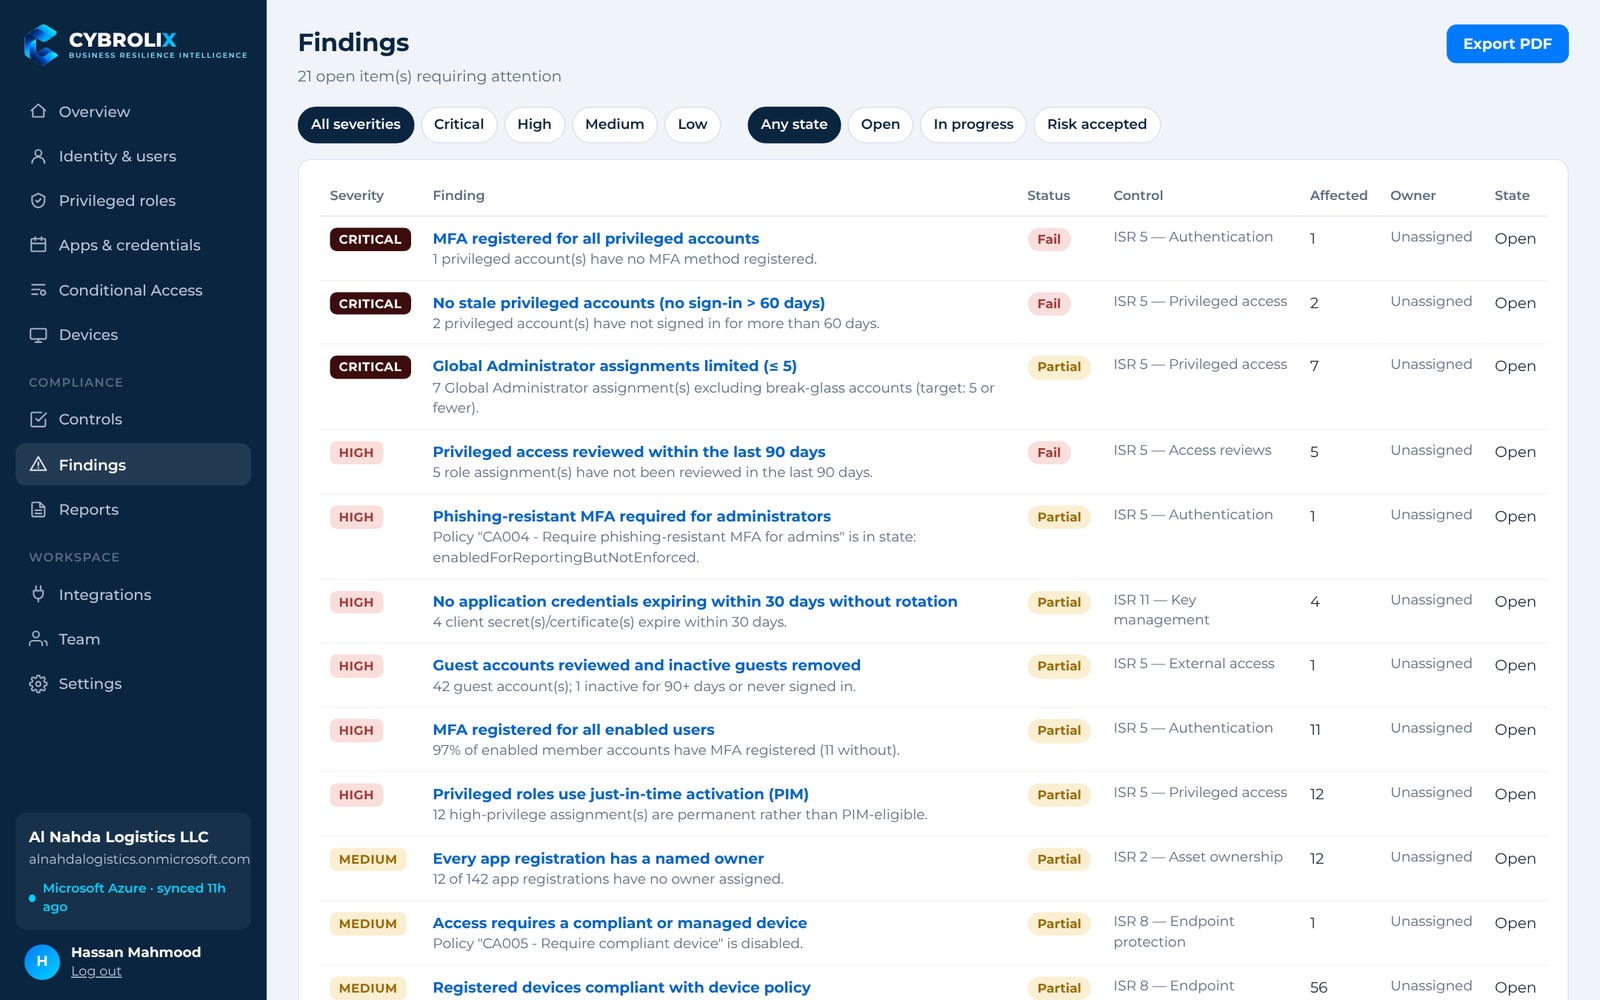
Learn more →Grant Cybrolix read-only access to Microsoft Entra ID and it continuously reviews the things auditors ask about first: who has privileged access, whether MFA is enforced, which app registrations and secrets are about to expire, and whether Conditional Access is doing its job.
ISR, UAE IA, UAE PDPL, SAMA, NCA and Qatar NIA — the regional standards, pre-mapped.
GDPR, NIS2, DORA and ISO standards for organisations operating in or selling to the EU.
SOC 2, NIST CSF, HIPAA, CCPA and FedRAMP for US and Canadian requirements.
ISO 27001, PDPA and sector regulations for teams across APAC.
Data protection and financial-sector frameworks across African markets.
LGPD and ISO-based programmes for organisations across the region.
Publish policies, send acknowledgement campaigns to staff and third parties, and track who has read what.
Run asset-, service- or scenario-based assessments with a pre-built risk and mitigation library.
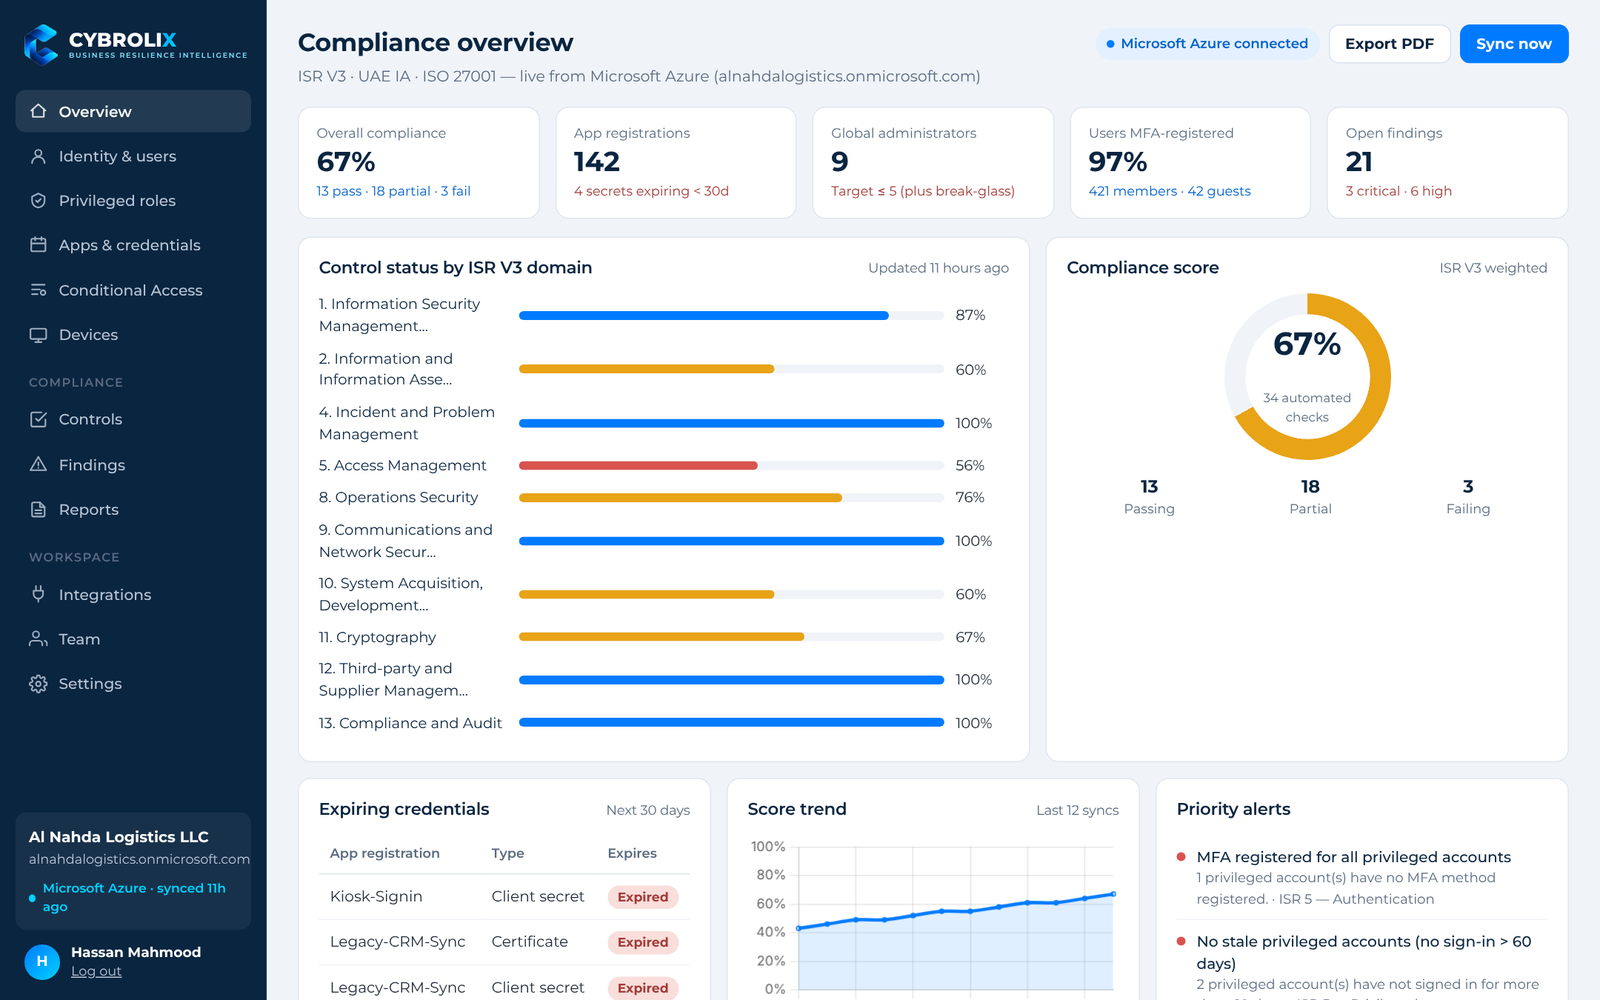
Follow implementation progress per control, per owner and per department, and export audit-ready reports.
Build trust and win deals by proving your security posture to customers and partners early.
Secure larger contracts and stay compliant with industry standards as you enter new markets.
Run many frameworks and business units from one platform and keep leadership informed in real time.
Cybrolix integrates with the technologies and processes behind your controls, measures them against defined thresholds and alerts you when a control drifts below its target maturity — long before an audit finding would.
Findings from your connected systems become risks automatically, with suggested mitigations drawn from a library spanning 100+ frameworks. Use your own methodology or ours, and show clients and regulators a living risk register rather than a yearly snapshot.
Start from pre-mapped controls instead of a blank spreadsheet.
Read-only cloud integration — no agents to install.
Screenshots and exports are replaced by continuous checks.
ISR, UAE IA, SAMA and NCA alongside global standards.
Every framework, every owner and every outstanding task in real time — with the technical evidence pulled straight from your cloud.
Get answers from people who have implemented these frameworks, right inside the platform.
Share your live security posture with customers and partners as a report.
Track security KPIs in real time and get alerts when they slip.
Technical and compliance support for every customer, in your time zone.
End-to-end automated assessments with your methodology or ours.
A native awareness module to educate staff on cyber hygiene.
Bring in assets from the tools you already use.
Assess vendors so their weaknesses do not become yours.
Evidence gathered across systems and documents without lifting a finger.
Discover how Cybrolix helps your organisation meet compliance standards, mitigate enterprise risks and work with less friction.
Create your accountDubai's Information Security Regulation is often described as "ISO 27001 for government". That is only half tr...
Privileged roles are the first thing an auditor looks at and the first thing an attacker looks for. This artic...
Most Azure tenants have dozens of app registrations with secrets nobody is tracking. When one expires, an inte...
Create a free account, connect Microsoft Azure, and watch Cybrolix map your environment to the controls that matter.